

Cybersecurity, governance & compliance for SMEs and mid-sized organisations
What I do is always the same: mapping out risks, translating them into plain language, and deciding together what needs to happen first.
The question differs, but the goal is the same: grip on risks and clear responsibilities. The three most common situations are

Your CISO is gone. The responsibility isn’t.
When security leadership becomes unavailable, I step in. Ensuring continuity from day one.

In the background. Present when it counts.
Not every organisation needs a full-time CISO. I provide oversight on risk, compliance and cyber resilience.

A clear route from assessment to outcome.
NIS2, ISO 27001 or the EU AI Act. Step by step towards a demonstrable outcome and lasting compliance.
01
Introductory conversation
30 minutes, no obligation. I listen to your situation and answer your questions. No sales pitch.
02
Assessment & Priorities
Together we define priorities, objectives and scope.
03
Execution
I work with you directly. No intermediaries, no junior consultants. What we agree on, I deliver.
04
Handover & Follow-up
Clear documentation and a structured handover. Your organisation can continue independently or choose a Tailored engagement.
Senior security leadership. One point of contact. Not a consultancy machine.
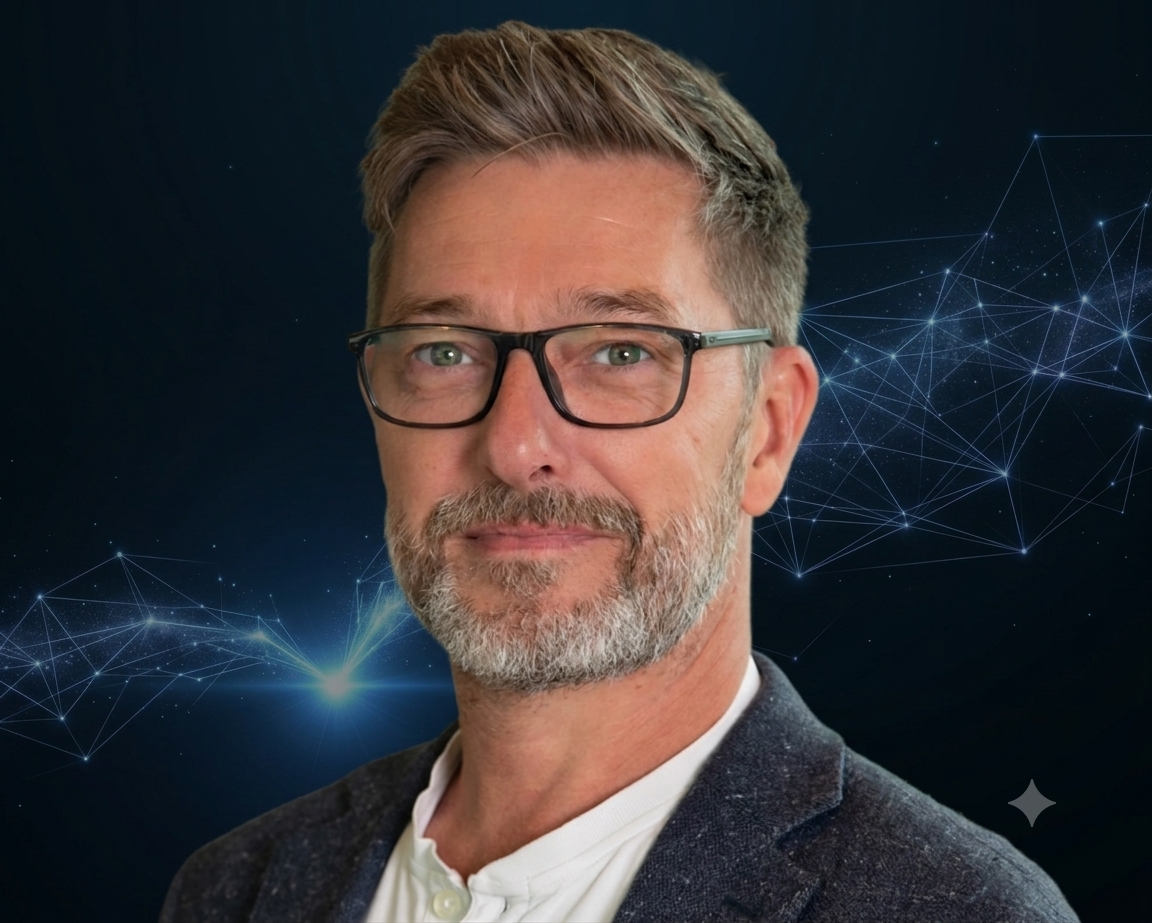
I’m Dennis Schut – cybersecurity professional, cloud architect and founder of GoodInit.
My career began at the Royal Netherlands Navy, where I spent six years working with military encryption and mission-critical communications – in an environment where reliability was absolute. I then worked at several startups, focused on technical consultancy, secure design and cloud architecture. This led to international leadership roles, including Chief Architect, CISO and Global SVP Cyberdefense. For more than fifteen years, I have advised boards, built security programmes, and helped organisations navigate cloud and cyber challenges in more than forty countries.
GoodInit isn’t an agency. Just me, with 30+ years of experience, sitting at the table with you. I map out what’s going on, translate it into plain language, and determine what needs to happen first.
Where specialist expertise is needed, I bring in trusted professionals from my network. So you get the right expertise, when you need it.
In technology, an ‘init’ is the initialisation: the first step that starts a system and makes everything that follows possible.
That’s exactly what good cybersecurity should be.
‘Good’ stands for quality. ‘Init’ stands for the foundation needed to grow safely, confidently and in control.
Every secure organisation begins with a good init.
-
Why NIS2 still affects your business even if you’re out of scope
Read the article →: Why NIS2 still affects your business even if you’re out of scopeThe Cyberbeveiligingswet, the Dutch implementation of the European NIS2 Directive, takes effect on 15 August 2026 and introduces registration, duty-of-care and reporting obligations for more than 8,000 Dutch organisations. Organisations that fall outside its scope often assume the topic isn’t relevant to them. That assumption may prove to be an expensive mistake. Article 21 requires…
AI Act 2026: transparency obligations from 2 August
Read the article →: AI Act 2026: transparency obligations from 2 AugustThe EU AI Act is not a law that switches “on” in a single day. It comes into effect in phases, which makes it difficult to keep track of what applies and when. On 2 August 2026, the transparency obligations under Article 50 come into effect: rules on AI chatbots, AI-generated content and deepfakes, which…
Six Persistent Myths About NIS2 in the Netherlands
Read the article →: Six Persistent Myths About NIS2 in the NetherlandsOn 7 July 2026, the Dutch Senate (Eerste Kamer) approved the Cyberbeveiligingswet, the Dutch implementation of the European NIS2 Directive. The law comes into force on 15 August 2026 and introduces new obligations for more than 8,000 organisations in the Netherlands. This means the law doesn’t only affect organisations that fall directly within its scope…
Let’s get acquainted
Do you have questions about cybersecurity, risks or compliance? Or are you facing a challenge you’d like to talk through? I respond within one business day.
A good conversation starts with a short question.
Amsterdam | Working throughout the Netherlands
info@goodinit.nl
Response within one business day
No obligation after the first conversation
Speak directly with Dennis Schut
Independent and pragmatic advice